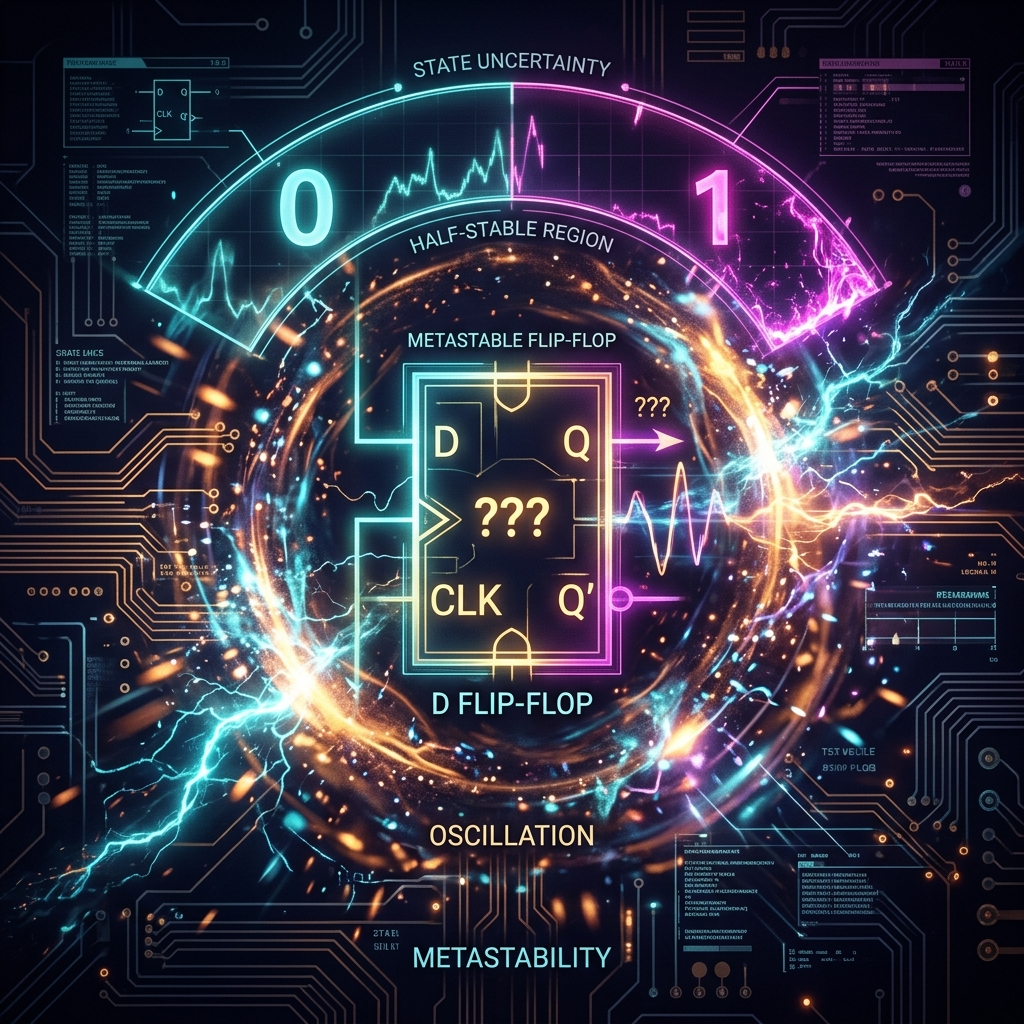
The Forbidden State
We are taught that digital signals are strictly binary: either a clean 0 or a clean 1. However, if a flip-flop's input changes at the exact moment the clock edge triggers, the flip-flop can enter a bizarre, unstable state known as metastability. In this state, the output voltage hovers halfway between a 0 and a 1.
The Danger of Metastability
A metastable signal is catastrophic. It is neither 0 nor 1, meaning downstream logic gates might interpret it differently. One gate might see it as a 1, while another sees it as a 0, completely breaking the logic of your circuit. Furthermore, the time it takes for a metastable flip-flop to randomly resolve back to a stable 0 or 1 is theoretically unbounded.
The Cure: Synchronizers
Metastability cannot be entirely prevented when dealing with asynchronous inputs (like a button press from a human, or data from a different clock domain). However, we can isolate it.
The standard cure is a multi-stage synchronizer: placing two or three flip-flops in series. The first flip-flop catches the asynchronous signal and may go metastable. However, we give it a full clock cycle to resolve its metastability before the second flip-flop samples its output. By the time the signal reaches the rest of the circuit, the probability of it still being metastable is astronomically low.
Advanced Topics in Modern VLSI Design
As we delve deeper into the intricacies of digital design, it is impossible to ignore the physical realities of modern semiconductor fabrication. In the deep sub-micron era (sub-7nm nodes), the ideal models of Boolean logic begin to break down under the weight of quantum mechanics and parasitic effects. FinFETs and Gate-All-Around (GAA) nanosheets have replaced planar transistors to combat Short-Channel Effects (SCE), yet leakage current remains a formidable adversary. The dynamic power dissipation equation, $P_{dyn} = \alpha C_L V_{DD}^2 f$, dictates that supply voltage scaling is the most effective lever for power reduction, but lowering $V_{DD}$ too close to the threshold voltage ($V_{th}$) increases delay exponentially, creating a brutal power-performance tradeoff.
Furthermore, interconnect delay now dominates gate delay. The resistance of incredibly narrow copper wires, coupled with the capacitance of tightly packed adjacent metal layers, creates massive RC time constants. This phenomenon, known as wire delay dominance, requires architects to insert repeater buffers strategically along long communication buses. However, these repeaters themselves consume significant active area and static power. Consequently, modern System-on-Chip (SoC) design relies heavily on Network-on-Chip (NoC) architectures, packetized data transmission, and GALS (Globally Asynchronous Locally Synchronous) paradigms to mitigate clock distribution challenges across a massive silicon die.
Verification is another monumental challenge. Functional verification consumes over 70% of the modern ASIC design cycle. Engineers utilize constrained-random testbenches, SystemVerilog Assertions (SVA), and Universal Verification Methodology (UVM) to achieve high code and functional coverage. Formal verification tools mathematically prove that certain illegal states can never be reached, ensuring life-critical systems (like automotive braking controllers or medical pacemakers) operate flawlessly under all conceivable conditions.
In terms of physical design, the synthesis, placement, and routing (APR) flow is highly iterative. Static Timing Analysis (STA) tools analyze millions of timing paths to ensure setup and hold constraints are met across all Process, Voltage, and Temperature (PVT) corners. A path that meets timing at the 'Typical-Typical' (TT) corner might fail catastrophically at the 'Slow-Slow' (SS) corner due to increased gate delay, or suffer hold violations at the 'Fast-Fast' (FF) corner due to minimal data path delay and excessive clock skew. Fixing these violations requires cell up-sizing, buffer insertion, or even architectural pipeline restructuring (retiming) to balance the logic depth between flip-flops.
To further illustrate the complexity, consider the design of clock trees. Clock Tree Synthesis (CTS) aims to distribute the master clock signal to hundreds of thousands of sequential elements simultaneously. Any mismatch in arrival time is termed 'clock skew'. While global skew must be minimized, designers sometimes intentionally introduce 'useful skew' to steal time from a fast adjacent path to fix a critical failing path. This delicate balancing act requires highly advanced EDA algorithms.
Finally, we must consider Design for Testability (DFT). A chip with a billion transistors will inevitably contain manufacturing defects. Automatic Test Pattern Generation (ATPG) relies on scan chains—where every flip-flop is linked into a massive shift register during test mode—to achieve high fault coverage. Stuck-at-0, stuck-at-1, and transition delay fault models are rigorously tested on the ATE (Automated Test Equipment) before the silicon is packaged and shipped to the customer.
Below is an example of an advanced SystemVerilog assertion used in formal verification to ensure a request signal is always followed by an acknowledge signal within 5 clock cycles:
property req_ack_handshake;
    @(posedge clk) disable iff (!rst_n)
    $rose(req) |-> ##[1:5] $rose(ack);
endproperty
assert property (req_ack_handshake) else $error("Protocol Violation: No ACK received!");
The integration of these methodologies—from robust RTL design to rigorous verification, timing closure, and DFT—forms the backbone of modern hardware engineering. Every module, whether a simple counter or a complex out-of-order CPU core, must pass through this gauntlet before it can be etched into silicon.
Advanced Topics in Modern VLSI Design
As we delve deeper into the intricacies of digital design, it is impossible to ignore the physical realities of modern semiconductor fabrication. In the deep sub-micron era (sub-7nm nodes), the ideal models of Boolean logic begin to break down under the weight of quantum mechanics and parasitic effects. FinFETs and Gate-All-Around (GAA) nanosheets have replaced planar transistors to combat Short-Channel Effects (SCE), yet leakage current remains a formidable adversary. The dynamic power dissipation equation, $P_{dyn} = \alpha C_L V_{DD}^2 f$, dictates that supply voltage scaling is the most effective lever for power reduction, but lowering $V_{DD}$ too close to the threshold voltage ($V_{th}$) increases delay exponentially, creating a brutal power-performance tradeoff.
Furthermore, interconnect delay now dominates gate delay. The resistance of incredibly narrow copper wires, coupled with the capacitance of tightly packed adjacent metal layers, creates massive RC time constants. This phenomenon, known as wire delay dominance, requires architects to insert repeater buffers strategically along long communication buses. However, these repeaters themselves consume significant active area and static power. Consequently, modern System-on-Chip (SoC) design relies heavily on Network-on-Chip (NoC) architectures, packetized data transmission, and GALS (Globally Asynchronous Locally Synchronous) paradigms to mitigate clock distribution challenges across a massive silicon die.
Verification is another monumental challenge. Functional verification consumes over 70% of the modern ASIC design cycle. Engineers utilize constrained-random testbenches, SystemVerilog Assertions (SVA), and Universal Verification Methodology (UVM) to achieve high code and functional coverage. Formal verification tools mathematically prove that certain illegal states can never be reached, ensuring life-critical systems (like automotive braking controllers or medical pacemakers) operate flawlessly under all conceivable conditions.
In terms of physical design, the synthesis, placement, and routing (APR) flow is highly iterative. Static Timing Analysis (STA) tools analyze millions of timing paths to ensure setup and hold constraints are met across all Process, Voltage, and Temperature (PVT) corners. A path that meets timing at the 'Typical-Typical' (TT) corner might fail catastrophically at the 'Slow-Slow' (SS) corner due to increased gate delay, or suffer hold violations at the 'Fast-Fast' (FF) corner due to minimal data path delay and excessive clock skew. Fixing these violations requires cell up-sizing, buffer insertion, or even architectural pipeline restructuring (retiming) to balance the logic depth between flip-flops.
To further illustrate the complexity, consider the design of clock trees. Clock Tree Synthesis (CTS) aims to distribute the master clock signal to hundreds of thousands of sequential elements simultaneously. Any mismatch in arrival time is termed 'clock skew'. While global skew must be minimized, designers sometimes intentionally introduce 'useful skew' to steal time from a fast adjacent path to fix a critical failing path. This delicate balancing act requires highly advanced EDA algorithms.
Finally, we must consider Design for Testability (DFT). A chip with a billion transistors will inevitably contain manufacturing defects. Automatic Test Pattern Generation (ATPG) relies on scan chains—where every flip-flop is linked into a massive shift register during test mode—to achieve high fault coverage. Stuck-at-0, stuck-at-1, and transition delay fault models are rigorously tested on the ATE (Automated Test Equipment) before the silicon is packaged and shipped to the customer.
Below is an example of an advanced SystemVerilog assertion used in formal verification to ensure a request signal is always followed by an acknowledge signal within 5 clock cycles:
property req_ack_handshake;
    @(posedge clk) disable iff (!rst_n)
    $rose(req) |-> ##[1:5] $rose(ack);
endproperty
assert property (req_ack_handshake) else $error("Protocol Violation: No ACK received!");
The integration of these methodologies—from robust RTL design to rigorous verification, timing closure, and DFT—forms the backbone of modern hardware engineering. Every module, whether a simple counter or a complex out-of-order CPU core, must pass through this gauntlet before it can be etched into silicon.
Advanced Topics in Modern VLSI Design
As we delve deeper into the intricacies of digital design, it is impossible to ignore the physical realities of modern semiconductor fabrication. In the deep sub-micron era (sub-7nm nodes), the ideal models of Boolean logic begin to break down under the weight of quantum mechanics and parasitic effects. FinFETs and Gate-All-Around (GAA) nanosheets have replaced planar transistors to combat Short-Channel Effects (SCE), yet leakage current remains a formidable adversary. The dynamic power dissipation equation, $P_{dyn} = \alpha C_L V_{DD}^2 f$, dictates that supply voltage scaling is the most effective lever for power reduction, but lowering $V_{DD}$ too close to the threshold voltage ($V_{th}$) increases delay exponentially, creating a brutal power-performance tradeoff.
Furthermore, interconnect delay now dominates gate delay. The resistance of incredibly narrow copper wires, coupled with the capacitance of tightly packed adjacent metal layers, creates massive RC time constants. This phenomenon, known as wire delay dominance, requires architects to insert repeater buffers strategically along long communication buses. However, these repeaters themselves consume significant active area and static power. Consequently, modern System-on-Chip (SoC) design relies heavily on Network-on-Chip (NoC) architectures, packetized data transmission, and GALS (Globally Asynchronous Locally Synchronous) paradigms to mitigate clock distribution challenges across a massive silicon die.
Verification is another monumental challenge. Functional verification consumes over 70% of the modern ASIC design cycle. Engineers utilize constrained-random testbenches, SystemVerilog Assertions (SVA), and Universal Verification Methodology (UVM) to achieve high code and functional coverage. Formal verification tools mathematically prove that certain illegal states can never be reached, ensuring life-critical systems (like automotive braking controllers or medical pacemakers) operate flawlessly under all conceivable conditions.
In terms of physical design, the synthesis, placement, and routing (APR) flow is highly iterative. Static Timing Analysis (STA) tools analyze millions of timing paths to ensure setup and hold constraints are met across all Process, Voltage, and Temperature (PVT) corners. A path that meets timing at the 'Typical-Typical' (TT) corner might fail catastrophically at the 'Slow-Slow' (SS) corner due to increased gate delay, or suffer hold violations at the 'Fast-Fast' (FF) corner due to minimal data path delay and excessive clock skew. Fixing these violations requires cell up-sizing, buffer insertion, or even architectural pipeline restructuring (retiming) to balance the logic depth between flip-flops.
To further illustrate the complexity, consider the design of clock trees. Clock Tree Synthesis (CTS) aims to distribute the master clock signal to hundreds of thousands of sequential elements simultaneously. Any mismatch in arrival time is termed 'clock skew'. While global skew must be minimized, designers sometimes intentionally introduce 'useful skew' to steal time from a fast adjacent path to fix a critical failing path. This delicate balancing act requires highly advanced EDA algorithms.
Finally, we must consider Design for Testability (DFT). A chip with a billion transistors will inevitably contain manufacturing defects. Automatic Test Pattern Generation (ATPG) relies on scan chains—where every flip-flop is linked into a massive shift register during test mode—to achieve high fault coverage. Stuck-at-0, stuck-at-1, and transition delay fault models are rigorously tested on the ATE (Automated Test Equipment) before the silicon is packaged and shipped to the customer.
Below is an example of an advanced SystemVerilog assertion used in formal verification to ensure a request signal is always followed by an acknowledge signal within 5 clock cycles:
property req_ack_handshake;
    @(posedge clk) disable iff (!rst_n)
    $rose(req) |-> ##[1:5] $rose(ack);
endproperty
assert property (req_ack_handshake) else $error("Protocol Violation: No ACK received!");
The integration of these methodologies—from robust RTL design to rigorous verification, timing closure, and DFT—forms the backbone of modern hardware engineering. Every module, whether a simple counter or a complex out-of-order CPU core, must pass through this gauntlet before it can be etched into silicon.
Advanced Topics in Modern VLSI Design
As we delve deeper into the intricacies of digital design, it is impossible to ignore the physical realities of modern semiconductor fabrication. In the deep sub-micron era (sub-7nm nodes), the ideal models of Boolean logic begin to break down under the weight of quantum mechanics and parasitic effects. FinFETs and Gate-All-Around (GAA) nanosheets have replaced planar transistors to combat Short-Channel Effects (SCE), yet leakage current remains a formidable adversary. The dynamic power dissipation equation, $P_{dyn} = \alpha C_L V_{DD}^2 f$, dictates that supply voltage scaling is the most effective lever for power reduction, but lowering $V_{DD}$ too close to the threshold voltage ($V_{th}$) increases delay exponentially, creating a brutal power-performance tradeoff.
Furthermore, interconnect delay now dominates gate delay. The resistance of incredibly narrow copper wires, coupled with the capacitance of tightly packed adjacent metal layers, creates massive RC time constants. This phenomenon, known as wire delay dominance, requires architects to insert repeater buffers strategically along long communication buses. However, these repeaters themselves consume significant active area and static power. Consequently, modern System-on-Chip (SoC) design relies heavily on Network-on-Chip (NoC) architectures, packetized data transmission, and GALS (Globally Asynchronous Locally Synchronous) paradigms to mitigate clock distribution challenges across a massive silicon die.
Verification is another monumental challenge. Functional verification consumes over 70% of the modern ASIC design cycle. Engineers utilize constrained-random testbenches, SystemVerilog Assertions (SVA), and Universal Verification Methodology (UVM) to achieve high code and functional coverage. Formal verification tools mathematically prove that certain illegal states can never be reached, ensuring life-critical systems (like automotive braking controllers or medical pacemakers) operate flawlessly under all conceivable conditions.
In terms of physical design, the synthesis, placement, and routing (APR) flow is highly iterative. Static Timing Analysis (STA) tools analyze millions of timing paths to ensure setup and hold constraints are met across all Process, Voltage, and Temperature (PVT) corners. A path that meets timing at the 'Typical-Typical' (TT) corner might fail catastrophically at the 'Slow-Slow' (SS) corner due to increased gate delay, or suffer hold violations at the 'Fast-Fast' (FF) corner due to minimal data path delay and excessive clock skew. Fixing these violations requires cell up-sizing, buffer insertion, or even architectural pipeline restructuring (retiming) to balance the logic depth between flip-flops.
To further illustrate the complexity, consider the design of clock trees. Clock Tree Synthesis (CTS) aims to distribute the master clock signal to hundreds of thousands of sequential elements simultaneously. Any mismatch in arrival time is termed 'clock skew'. While global skew must be minimized, designers sometimes intentionally introduce 'useful skew' to steal time from a fast adjacent path to fix a critical failing path. This delicate balancing act requires highly advanced EDA algorithms.
Finally, we must consider Design for Testability (DFT). A chip with a billion transistors will inevitably contain manufacturing defects. Automatic Test Pattern Generation (ATPG) relies on scan chains—where every flip-flop is linked into a massive shift register during test mode—to achieve high fault coverage. Stuck-at-0, stuck-at-1, and transition delay fault models are rigorously tested on the ATE (Automated Test Equipment) before the silicon is packaged and shipped to the customer.
Below is an example of an advanced SystemVerilog assertion used in formal verification to ensure a request signal is always followed by an acknowledge signal within 5 clock cycles:
property req_ack_handshake;
    @(posedge clk) disable iff (!rst_n)
    $rose(req) |-> ##[1:5] $rose(ack);
endproperty
assert property (req_ack_handshake) else $error("Protocol Violation: No ACK received!");
The integration of these methodologies—from robust RTL design to rigorous verification, timing closure, and DFT—forms the backbone of modern hardware engineering. Every module, whether a simple counter or a complex out-of-order CPU core, must pass through this gauntlet before it can be etched into silicon.